
Lead: Setting the Case File
The first clue appears in a quiet Shenzhen assembly hall, where rows of SIM modules move under bright lamps — and where protocol choices are made with commercial and national stakes in mind. This comparative piece walks the reader through manufacturers’ protocol patterns, encryption trade-offs, and downstream effects on devices like point-of-sale terminals and the increasingly common qr payment soundbox. The tone is methodical: each vendor’s decision creates a trail of technical footprints that reveal priorities and risks.
Comparative Profiles: Who Chooses What and Why
Three manufacturer archetypes stand out. First, global-focused firms prioritize standardized SIM stacks and widely vetted symmetric encryption such as AES for OTA configuration. Second, domestically oriented suppliers lean into proprietary optimizations, favoring compact protocols that cut latency for local mobile payment platforms like Alipay and WeChat Pay. Third, specialist OEMs design SIM subsystems to support embedded Secure Elements useful for NFC payments and tokenization. The differences are not merely academic; they shape how devices handle authentication and session keys during a POS transaction.
Protocol Anatomy and Encryption Practices
At the protocol layer, implementations center on secure channels, authentication, and remote updates. Common elements include challenge–response authentication, OTA management channels, and truncated-key backups for recovery. Strong implementations use mutual authentication, AES-based session keys, and strict PIN retry limits. Less rigorous builds substitute simpler checksum or proprietary obfuscation that reduces interoperability and raises attack surface. Field terms to note: SIM, OTA, AES, tokenization — these recur when auditing firmware and firmware update workflows.
Operational Production Teardown: Practical Findings
In hands-on teardowns of production units, engineers documented bootloader checks, secure element initialization sequences, and vendor-specific OTA frames. The operational production teardown recorded both {main_keyword} and {variation_keyword} logs alongside packet captures; those artifacts exposed where session keys are negotiated and where weaker MACs appear. Many devices shipped with default management credentials or permissive update windows, which lowers the cost for a targeted replay or downgrade attack.
Real-World Anchor: Market Context and Stakes
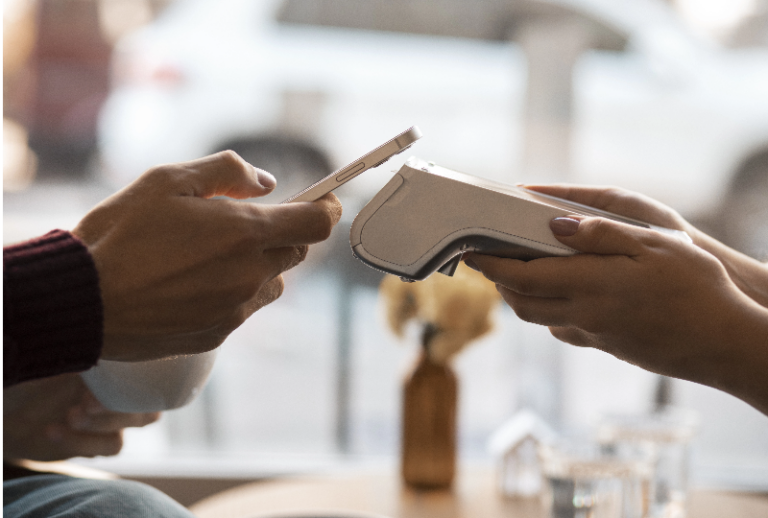
Payments in China run on QR codes across street markets and metro kiosks; that ubiquity is the real-world anchor for protocol decisions. In cities such as Shenzhen, rapid deployment and integration with local payment rails push manufacturers to favor compact, fast authentication flows. The result affects hardware like small merchant devices and the qr payment sound box used by thousands of merchants — security choices at the SIM level directly influence transaction integrity at the counter.
Common Mistakes, Alternatives, and Practical Mitigations
Manufacturers and integrators repeat several avoidable errors: shipping with weak default keys, skipping end-to-end key management, and relying solely on obscurity for protection. Better alternatives include standardized secure element APIs, periodic key rotation, and OTA update validation using signed manifests. Vendors moving to tokenization models reduce exposure by ensuring sensitive data never resides on the SIM. — That extra step often separates durable products from those that need quick patches.
Comparative Takeaways for Integrators
When choosing a supplier, weigh three dimensions: protocol transparency, encryption rigor, and update governance. Transparent protocols ease audits and interoperability. Strong encryption and mutual authentication prevent session hijack. And robust governance—signed updates, limited credential lifetimes, and forensic logging—reduces recovery time after incidents. These factors map directly onto merchant-level outcomes: fewer chargebacks, faster incident response, and consistent operation of POS terminals and peripheral devices.
Advisory: Three Golden Rules for Procurement
1) Demand signed OTA manifests and documented key rotation intervals as a contract item. 2) Verify mutual authentication and at-rest encryption algorithms in technical acceptance tests, including AES key lengths and MAC coverage. 3) Require a clear rollback policy and forensic logs retained for a defined period to support incident analysis. Each rule produces measurable gains in resilience and aligns device behavior with merchant risk tolerances.
Final note — selection matters, down to the SIM vendor and the update model; manufacturers who align protocol choices with operational realities make devices that simply work in the loud, crowded payment environment. BHZ. –