
The problem: identity gaps are a real bottleneck
Cities, factories, and utilities are getting smarter fast, but that speed hides a messy truth: devices still too often rely on weak identities. When a sensor, gateway, or camera boots with insecure credentials, the network is exposed. That’s where a robust approach to device identity — paired with reliable connectivity like an iot sim card — moves from nice-to-have to mission-critical. IDC estimated about 41.6 billion connected IoT devices by 2025, which means the attack surface scales dramatically if identities aren’t locked down.
Why secure digital identity actually fixes more than one problem
A clear device identity enables trusted onboarding, automated updates, and precise access control. With eSIM or traditional SIM options, you can tie device identity to a lifecycle: manufacturing, provisioning, field operation, and decommissioning. That lifecycle approach reduces manual secrets management and limits blast radius after a breach. It also makes maintenance predictable — OTA updates and SIM provisioning become straightforward rather than risky.
Where systems typically fail
Common failures are simple and human-driven: default passwords left in place, device keys stored unprotected, or operators using a single APN for everything. Those choices let attackers move laterally across M2M networks. The bigger systems-level failure is blind trust — assuming a device is who it claims to be without cryptographic checks or real-time attestation. Fixing this requires identity-first design paired with secure connectivity.
What to build: practical components that matter
Start with three concrete pieces: immutable device identity, secure provisioning, and ongoing attestation. Immutable identity often uses hardware-backed keys or eSIM profiles tied to a vendor-managed trust anchor. Secure provisioning means scripts and servers that deliver credentials through encrypted channels. Ongoing attestation checks device state before granting access — think lightweight device authentication that runs each session. These elements work with M2M connectivity to keep endpoints honest.
Operational production teardown
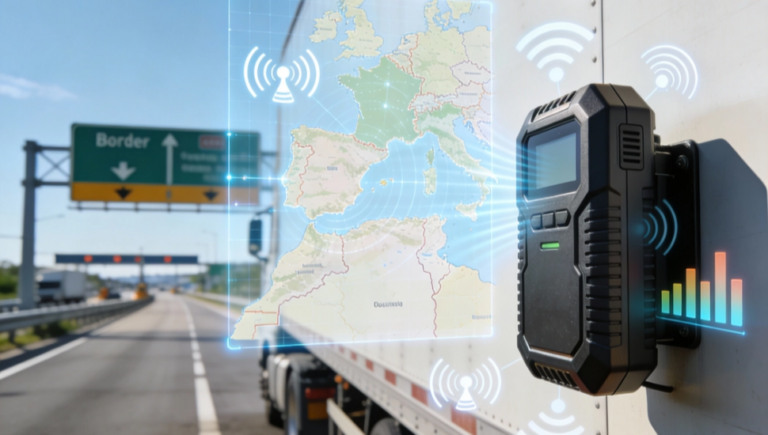
In a real deployment you’ll see stages: assembly, secure boot provisioning, network attachment, and lifecycle revocation. At assembly, a unique device key is burned or injected via a secure element. During provisioning, the platform performs OTA updates and binds SIM profile and APN settings. In the live fleet, health checks and attestation reduce risk. When retiring devices, revoke the profile and wipe credentials. This is where {main_keyword} and {variation_keyword} belong in the operational production teardown — not as buzzwords, but as checkpoints in a controlled pipeline. Integrating a trusted m2m iot sim card ties network identity to device identity cleanly.
Common mistakes to avoid
Teams often push connectivity live without a revocation plan, or they centralize trust in a single cloud tenant. Both lead to long-term exposure. Another trap: treating identity as an add-on. Identity must be part of the architecture from the start. Small fixes like rotating keys, enforcing hardware-backed credential storage, and validating APN usage remove a lot of risk without huge overhead — and they scale.
How to vet vendors and tech — three golden rules
1) Proof of lifecycle controls: confirm the vendor documents how identities are generated, provisioned, and revoked, with logs you can audit. 2) Network tie-in and portability: ensure SIM profiles or eSIM management can move between operators and support secure OTA. 3) Measurable attestation: the provider should offer device health checks and session-level authentication with clear metrics for false positives and recovery time.
Advisory close: three critical evaluation metrics
Measure these before you commit: mean time to revoke (how fast a compromised device is cut off), cryptographic key protection level (hardware-backed vs. software-only), and coverage of OTA security checks (percentage of fleet receiving validated updates). These metrics give concrete guardrails for safe rollouts and ongoing operations. When you want an integrated approach that pairs connectivity, identity, and lifecycle controls, consider solutions that demonstrate those metrics in real deployments — because that’s where value shows up. BHDC. —